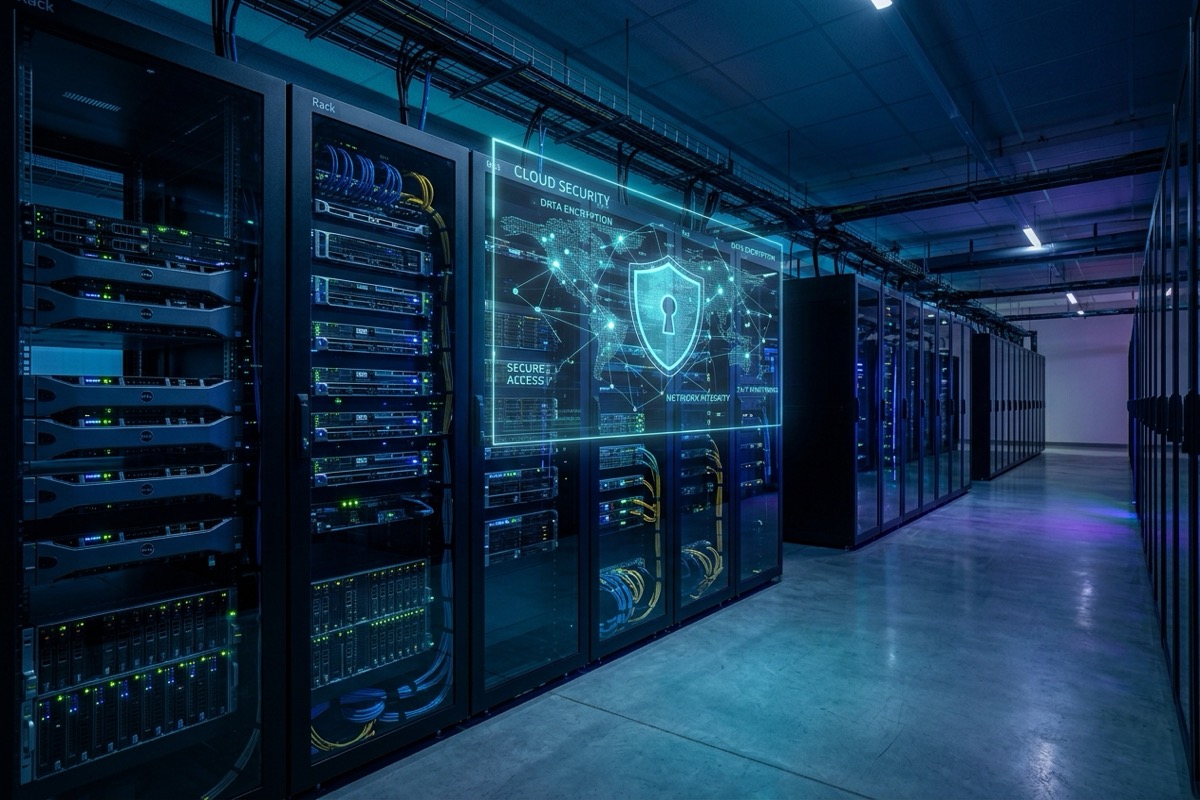
As businesses in Ghana migrate their legacy servers to cloud environments, security is often a chief concern. A common misconception is that offsite hosting is inherently less secure than physical servers in your office. In reality, data centers provide security levels that few small-to-medium enterprises can match locally.
The Shared Responsibility Model
Security in the cloud operates on a shared responsibility framework. The data center provider secures the physical hardware, power grids, and hypervisors. You, the client, are responsible for securing access policies, customer databases, and operating systems. Partnering with a managed service provider ensures your side of the contract is properly handled.
Hardening Access Control Policies
Most cloud security breaches originate from compromised user credentials. Implementing Multi-Factor Authentication (MFA) across your virtual networks is the single most effective defense against unauthorized access. Additionally, access should be governed by the principle of least privilege: employees should only access files and settings necessary for their immediate work.
Secure Configurations and Firewalls
Unused open server ports are a primary entry point for automated exploits. Cloud hosts must be protected by Next-Generation Firewalls configured to inspect traffic, block suspicious IPs, and route admin access through secure Virtual Private Networks (VPNs). Regular software updates and patch regimes on virtual systems are critical to closing hardware vulnerabilities.